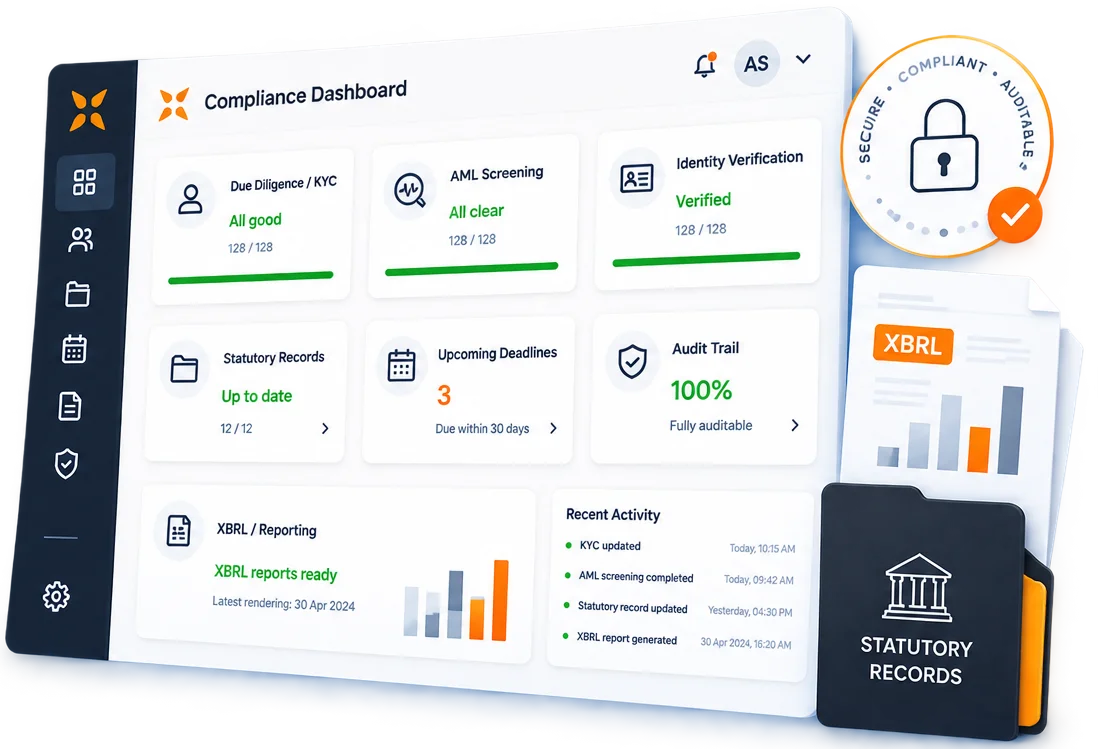
Manage due diligence, screening, statutory records, regulatory obligations and review deadlines from one system. Episcript builds custom corporate and regulatory compliance software for organisations that manage obligations across many entities and cannot rely on spreadsheets to prove what was done. AI features can be added later to read documents and flag gaps.
Built in Singapore for compliance teams, corporate service providers and accounting firms.
Onboarding, identity checks, screening, risk assessment, monitoring and reporting run from one client file, with the evidence and the reviewer recorded at each stage. Company administration and ACRA filings sit in our corporate secretarial software, which can share the same entity record.
The whole due diligence file sits against the person or entity it concerns: identification, proof of address, source of funds, screening results and the risk rating. Open the record to see the current position, including what expires next.
Screening runs through the provider you already subscribe to, where it publishes an API, and results return to the record. A match goes to the reviewer your policy names, and the decision is kept with its reasoning.
Clients verify their identity in one of two ways: through Singpass where it suits them, or through your own live capture where it does not.
Where the use case is eligible and approved, clients verify through Singpass instead of emailing documents. The pass or fail result files against the record with a timestamp, and we confirm the route open to you during scoping.
For foreign directors, shareholders and anyone outside Singpass, the subject takes a live photo, the system matches it to their passport or ID, and both images file against the record.
A staff member approves or rejects each result, and every attempt is logged with the user, the method and the outcome.
These records hold who each entity is, who runs it and who owns it, and your screening and your registers draw on them.
Every entity keeps one record: incorporation particulars, UEN, SSIC codes, financial year end, addresses, service tags and key dates. Search the whole portfolio, and change a detail once for every register, document and report to pick it up.
Directors, company secretaries and other officers sit against the entity with their appointment dates, identity documents and files. Each officer is also a due diligence subject, so their verification and screening results show on the same screen.
Individual and corporate shareholders share one module, with share records, certificates and allotment history. Ownership through a corporate shareholder stays traceable up to the controller at the top, supporting the register of members and beneficial ownership work.
Track issued and paid-up capital by share class and currency. Allotments and class changes update the register of members and the certificates, and past positions stay readable for any date.
Registers generate from the entity record and update in real time. Nobody maintains a parallel spreadsheet, and nobody discovers at year end that the two versions disagree.
Every corporate change keeps its own history beside the registers, and you can export any register when a regulator, an auditor or a bank asks for it.
Maintaining regulatory compliance takes more than due diligence. A regulated firm also answers for its AML policy, PDPA duties, staff training, outsourcing arrangements and whatever its own board has committed to, and each of those needs an owner, a control and proof that the control actually ran.
We build that regulatory compliance programme into the same platform as your client records. When a regulator or an auditor asks how you stay compliant, the answer starts from a live register rather than a week spent searching shared drives.
Every obligation your organisation carries, from the Companies Act and the Corporate Service Providers Act to MAS notices and your own policies, recorded with its source, its owner and the control that meets it.
Checks and attestations scheduled at the frequency each control needs, say quarterly for a sanctions list refresh and yearly for staff training, with the result and its evidence filed against the obligation.
A failed check or a missed review opens an issue with a severity, an owner and a date for the fix. It stays open until someone closes it with evidence, not with a note saying it was sorted.
Before an inspection or an internal audit, run one compliance readiness report: every obligation, when its control was last tested, any open issues and the evidence behind each, exported as a single pack.
These modules watch the calendar and the log, which between them answer what is due, what is late and what changed.
Track AGM, annual return, ECI and GST dates alongside your own review cycles. Reminders go by email, WhatsApp or SMS on the lead time and wording you set, with delivery tracked and a dashboard showing what is due and what has slipped.
Report on tax progress, AGM status, KYC completeness, open compliance issues, unassigned entities or any filter you set. Run reports on demand or schedule them for the monthly meeting, straight from live records.
Every edit, approval, deletion and record view is logged automatically with the user and the time. Finding who changed a record takes one search, and the log exports straight into the audit file.
Run a share transfer, address change or financial year update as an action, with its stage, owner and documents in view. Completed changes stay readable in the entity history.
The system prepares the annual report and generates the XBRL file itself, ready for submission through BizFile.
Load the figures for the entity and map the accounts once. The mapping holds for next year.
Work through the guided set, with last year's answers carried forward for editing.
The system builds the financial statements and the notes from the mapped data.
Circulate the draft, record the comments and keep each version with its author.
The file builds from the same mapped data, and your team submits it through BizFile.
Documents draft themselves from data already held, travel out for signature, and file back where the evidence belongs.
Resolutions, declarations, forms, agreements and certificates draft from the entity record using your own templates. Your team reviews each draft before it goes out.
Send documents for signature and track them to completion. Signing uses a one-time password, works on a phone and handles bulk dispatch, with each signature recorded against a verified identity.
Generated and uploaded files sit in structured folders against the entity, with tags, version control and role-based access. Finding a document takes one search.
Compliance work stalls when it waits on a client. The portal turns that wait into something you can see and chase.
Clients sign in to download documents, read invoices, answer requests, upload identity documents and complete your forms. They see only their own records, and every action is logged against the client, so a missing document shows as a status rather than a chain of emails.
The modules above carry the compliance work. Behind them sits the wider library. We switch on what you need, quote the rest as later phases, and build anything you run that is not listed here.
Fees raised, chased and reconciled against the client record.
Raise invoices for retainers, compliance reviews or one-off work directly from the client file. Track payments, issue reminders and draw reports by client or by service. Organisations billing well beyond compliance work can widen this into our invoicing software.
Service agreements held with their fees, durations, renewal dates and termination terms. Active, terminated and reinstated agreements each carry their own status, and the system validates the dates rather than trusting a typed entry.
Who is doing what, where it is filed, and what arrived by post.
Log a conversation, assign a task, set the deadline and attach the discussion to the client or the record it concerns. A reviewer picking up a file reads the context rather than asking the colleague who handled it last.
Search across people, entities, roles, KYC status, billing and compliance history from one interface. Filter on any condition you set: entities overdue for review, controllers with an expired identity document, clients screened before a given date.
Log incoming mail against the entity, notify the client, forward it and record the outcome. Collections require identity verification before anything leaves the office, and the activity report shows every item handled over any period you choose.
Reaching clients on the channel they actually read.
Send document requests and status updates through WhatsApp Business or SMS, not only deadline reminders. Every message logs against the client, which matters when a deadline passes and the file has to show what was sent.
Run campaigns to your client list using branded templates and filters. Announce a regulatory change, circulate a newsletter or warn a segment about an approaching deadline, then read the engagement figures afterwards.
Enquiry forms on your website and social channels drop straight into the system. Each enquiry lands with a follow-up owner and a status, and you can see how many enquiries became clients from the records themselves rather than from a spreadsheet somebody updates by hand.
These are the AI features we build into a compliance system, each scoped with you and built in its own phase. Every one works with information already held in your system, and you watch it run before it goes live.
AI reads an incoming identity document, certificate or letter and lifts the names, dates, addresses and figures from it. Your staff confirm the values before anything updates a record.
AI sorts screening hits by how closely they match the subject you hold, and drafts a short note on each one. A reviewer still decides, and the decision files with the reasoning.
AI scans entity records for what is missing or inconsistent: a controller without particulars, an expired identity document, an officer with no verification result. Each finding lands as a task.
AI ranks the entities needing attention this week, weighing risk rating, review dates, filing status and how long a request has waited on a client response.
AI summarises a compliance file before a periodic review: the current officers, the ownership chain, recent changes, screening history and anything outstanding, drawn from your own records.
AI answers client questions inside the portal using information from their own file. Anything it cannot answer routes to the staff member handling that client.
We scope each connection against the platforms your organisation already uses. Where a screening provider, accounting package or signing service publishes a suitable API, we can quote that integration as part of the build.
How a custom corporate compliance system compares with an off-the-shelf compliance platform.
| Point of comparison | EpiscriptCustom build | Typical productOff-the-shelf platform |
|---|---|---|
| Fit to your compliance controls | Built around your policy, risk bands, approvals and review cycles | Configured within the workflows, rules and options the platform supports |
| Obligations and compliance programme | Obligations, controls and monitoring plan written around your own regulators and policies | Ready-made obligation libraries and templates, strongest where your framework matches the product's |
| Due diligence and screening | Connects to the screening provider you choose, where a suitable API is available | Provider choice and pricing depend on the platform's supported integrations or bundled services |
| Identity verification | Supports approved Singpass routes, live capture and document matching | Identity verification depends on the platform and its supported Singapore integrations |
| Singapore registers and filings | Modules built around Singapore records such as the RORC and nominee registers | Coverage varies according to the markets and jurisdictions the product supports |
| XBRL and annual reporting | Generates XBRL output from the same controlled data set where included in scope | May be built in, integrated, or handled through a separate preparation tool |
| Evidence and audit trail | Audit evidence follows your own record structure, permissions and reporting needs | Audit trails generally follow the structure and export formats the product supports |
| Adding a module later | Additional modules designed and quoted as later phases | Additional functionality depends on available modules, APIs and the vendor roadmap |
| AI features | Scoped around your own data, controls and human review process | AI capabilities depend on what the platform provides and how much configuration it allows |
| Commercial model | Usually project-based, with hosting, support and licensing defined in the agreement | Usually subscription-based, often by user, entity, module or usage |
Swipe to see the full table
A focused first phase, usually entity records, due diligence and reminders, can go live within weeks. Later phases each get their own quote and release.
We walk through your compliance policy, risk bands, approval steps and document wording, then agree what the first phase covers.
You review working screens as they arrive rather than a written specification. Changes cost least at this point.
We map your spreadsheets or your current system, run a test import for you to check, then load the live data.
Your staff train on their own records. Support continues after handover, by phone, email or video call.
Corporate secretarial software runs company administration: incorporation, ACRA filings, statutory registers, AGMs and corporate documents. Corporate compliance software covers the wider obligation: due diligence, identity verification, AML screening, risk ratings, monitoring, evidence and regulatory reporting. Many organisations run both, on one platform, with the entity record shared between them.
It should hold every obligation your firm carries, name an owner and a control for each, schedule the checks that prove the control works and keep the evidence beside it. For a Singapore corporate service provider that usually spans AML and CDD, PDPA and ACRA filings, plus MAS notices for a regulated financial firm, with a readiness report available before any inspection.
Yes. We build the due diligence workflow around the policy your organisation already applies: the documents you collect, the checks you carry out, the risk rating you assign, the reviewer who approves it and the review dates that follow. Screening results, expiry dates and KYC status file against each individual and entity. The obligation stays with your organisation, and the system keeps the record.
The system connects to the screening provider your organisation already subscribes to, where that provider publishes a suitable API. We scope the connection during the build and quote it as part of the project. Episcript does not resell a screening service, so you keep your existing contract, your existing data sources and your existing per-check pricing.
Identity verification runs two ways. Singpass-enabled verification can be integrated where the use case is eligible and approved, since the higher-assurance Singpass routes are restricted and subject to approval. Everyone else, including foreign directors and shareholders, uses our own live facial capture with passport or identity document matching. A staff member approves or rejects each result, and every attempt writes to the verification log.
Yes. The system generates the XBRL file itself, ready for submission through BizFile. You import the trial balance, map the accounts once, complete the guided disclosures, and the annual report and the XBRL file both build from that single data set. Version control keeps each draft, and the audit trail records who changed what along the way.
Statutory dates are tracked per entity, covering AGM, annual return, ECI and GST, alongside your own review cycles and document expiry dates. Reminders leave by email, WhatsApp or SMS on the lead time you set, with delivery tracked. A dashboard separates what falls due from what has already slipped, and alerts fire when something passes without action.
Every edit, approval, deletion and record access writes to the log with the user and the timestamp. The trail runs in the background rather than depending on staff to record anything. You can filter it by entity, by user or by date range, then export the result for an audit file, an internal review or a regulator's request.
Yes. The client portal handles document downloads, invoices, reminders, form submissions and uploads. Clients supply the identity documents your due diligence needs without sending them by email. Access reaches their own records only, and every portal action writes to the log against that client, which shows who supplied what and when.
Yes. We map your spreadsheets or your current database to the new structure, clean the data with you, then load entity records, officers, shareholdings, due diligence files and document history. You check a test import before the live run. Nothing is dropped without your sign-off, and the old system stays available until you are satisfied.
Yes. Most teams begin with entity records, due diligence and reminders. Identity verification, registers, XBRL preparation, the client portal, reporting and AI features follow in later phases. Each phase is quoted and released on its own, which spreads the cost across your financial year and keeps the first release small enough to test properly.
The system prepares the records, annual report information and XBRL file the filing workflow needs. Submission itself still takes place through ACRA BizFile, and the generated file is prepared for that process. Where a direct integration is available for a particular transaction, we assess it as part of the project scope.
Hosting is scoped around your organisation's security, deployment and data residency requirements, and the system can be deployed on Singapore-based infrastructure where you need it. Access is granted by role and by client, documents carry their own permissions, and activity logs record who viewed or changed a record. Those controls support your PDPA obligations alongside your own policies, and responsibility for meeting them stays with your organisation.
Yes. Our solutions are eligible for government grants, and software costs form part of the transformation schemes. We will explain how your project fits and prepare the documents an assessor expects to see.
Finance, operations and reporting on one platform, where compliance is one function among several.
Read more Corporate secretarial softwareIncorporations, registers, resolutions and annual returns, with every document generated from the same company record.
Read more Custom CRM softwareA full sales pipeline for firms winning corporate work, with lead scoring, lead assignment and campaign tracking.
Read moreCompliance teams usually know exactly where their current setup falls short: the identity document that expired without anyone noticing, the screening result sitting in someone's inbox, the audit request that takes a week of searching to answer. Book a demo and we will walk through the system with a real file.